Cloud Security Lab
An end-to-end attack, detect, and respond lab across AWS and Kubernetes, executing a full MITRE ATT&CK kill chain and the detection and response controls that catch it.
AWS
ArchitectureOpen full size ↗
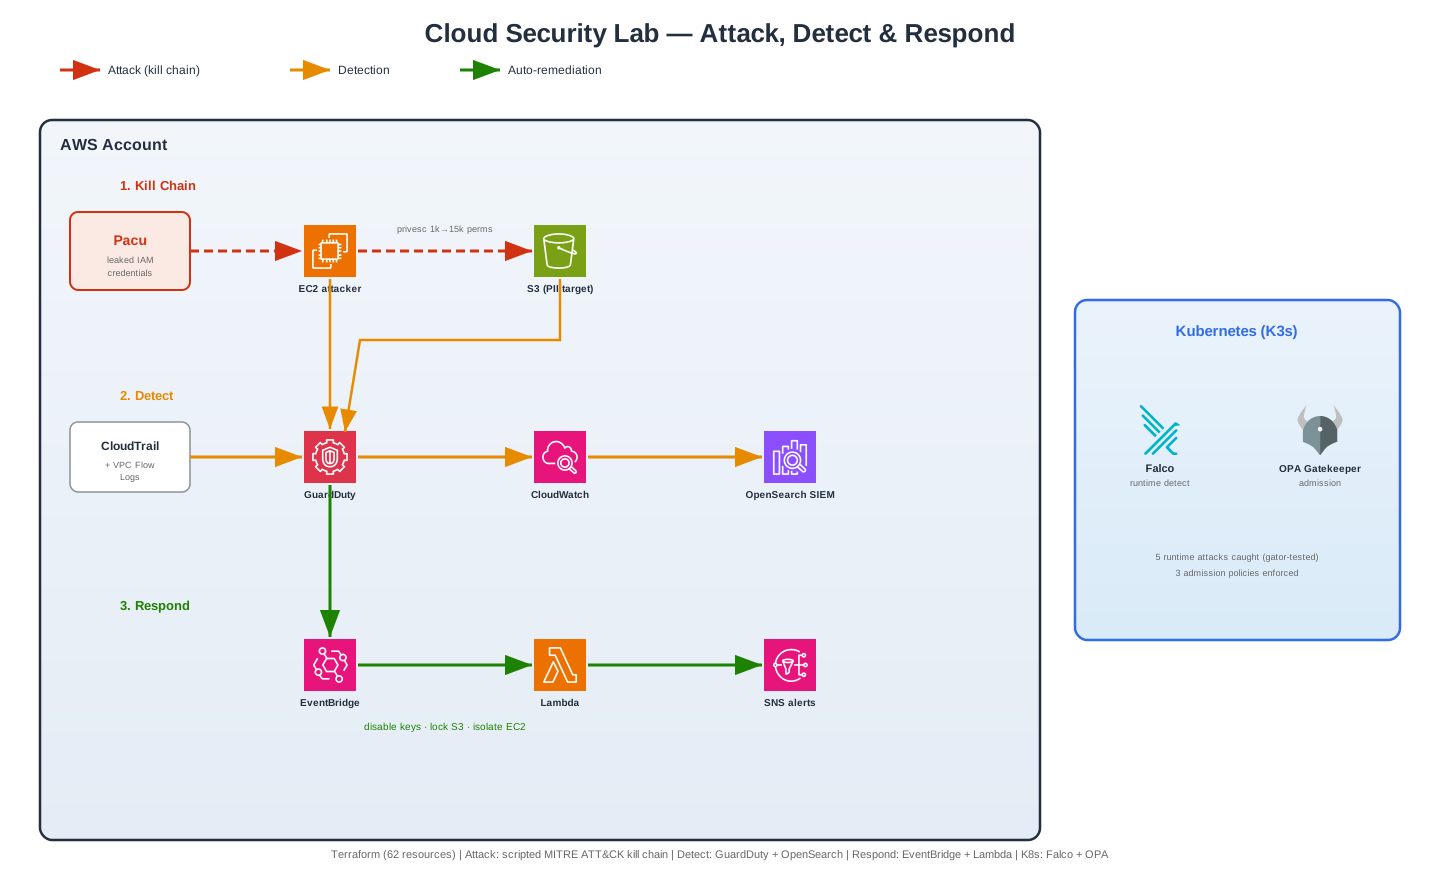
How it flows
 Paculeaked IAM creds
 PrivEsc1k → 15k perms
 S3 Exfil + STSlateral movement
 CloudTrail+ VPC Flow Logs
 OpenSearchkill-chain SIEM
 GuardDutyIAM threat
Falco + OPAK8s runtime
 EventBridge λdisable keys
Problem
Detection rules are only trustworthy if you have seen them fire against a real attack. This lab builds both sides: an offensive kill chain and the defensive controls that should catch it, so detection efficacy is demonstrated rather than assumed.
Attack
- The full MITRE ATT&CK kill chain is scripted under attack/ so it runs identically every time and always under the leaked credential rather than an admin identity: initial access, permission enumeration, then privilege escalation from 1,039 to 15,319 permissions via policy attachment.
- Then S3 exfiltration of staged PII and lateral movement via STS role assumption, with Pacu and ScoutSuite available for deeper manual exploration.
Detect & Respond
- CloudTrail and VPC Flow Logs feed an OpenSearch SIEM with a kill-chain correlation dashboard.
- GuardDuty findings on IAM threats trigger an EventBridge rule that fires a Lambda to automatically disable compromised access keys.
- On Kubernetes, Falco runs as a DaemonSet catching runtime attacks: shell spawning, sensitive file reads, unauthorized binary execution, and container escape via host mount.
- OPA Gatekeeper blocks privileged containers, host namespace access, and root execution across all non-system namespaces.
Detection as Code
- The Gatekeeper admission policies are unit-tested with gator against known-good and known-bad pods, so a broken policy fails CI before it ever reaches a cluster.
- CI gates selectively against a codebase that is vulnerable on purpose: the defensive modules are held to a Checkov baseline that blocks new misconfigurations, the intentionally-vulnerable surface is scanned informationally, and secret scanning blocks everywhere.
- The exercised techniques are captured as an importable MITRE ATT&CK Navigator layer.
Outcome
A closed loop from exploitation to automated containment, with every control demonstrated against a live, reproducible attack rather than described in the abstract.
62 Terraform resources across 7 modules, deployable and destroyable on demand.
Live run receipt
- Provision
- 62 Terraform resources across 7 modules, AWS plus Kubernetes
- Attack
- Pacu kill chain escalated 1,039 to 15,319 permissions and exfiltrated staged PII
- Detect
- Falco caught 100% of simulated runtime attacks, OpenSearch correlated the kill chain
- Respond
- GuardDuty finding fired EventBridge, Lambda disabled the compromised key
- Coverage
- Attack · Detect · Respond